 INFRA
INFRA

INFRA

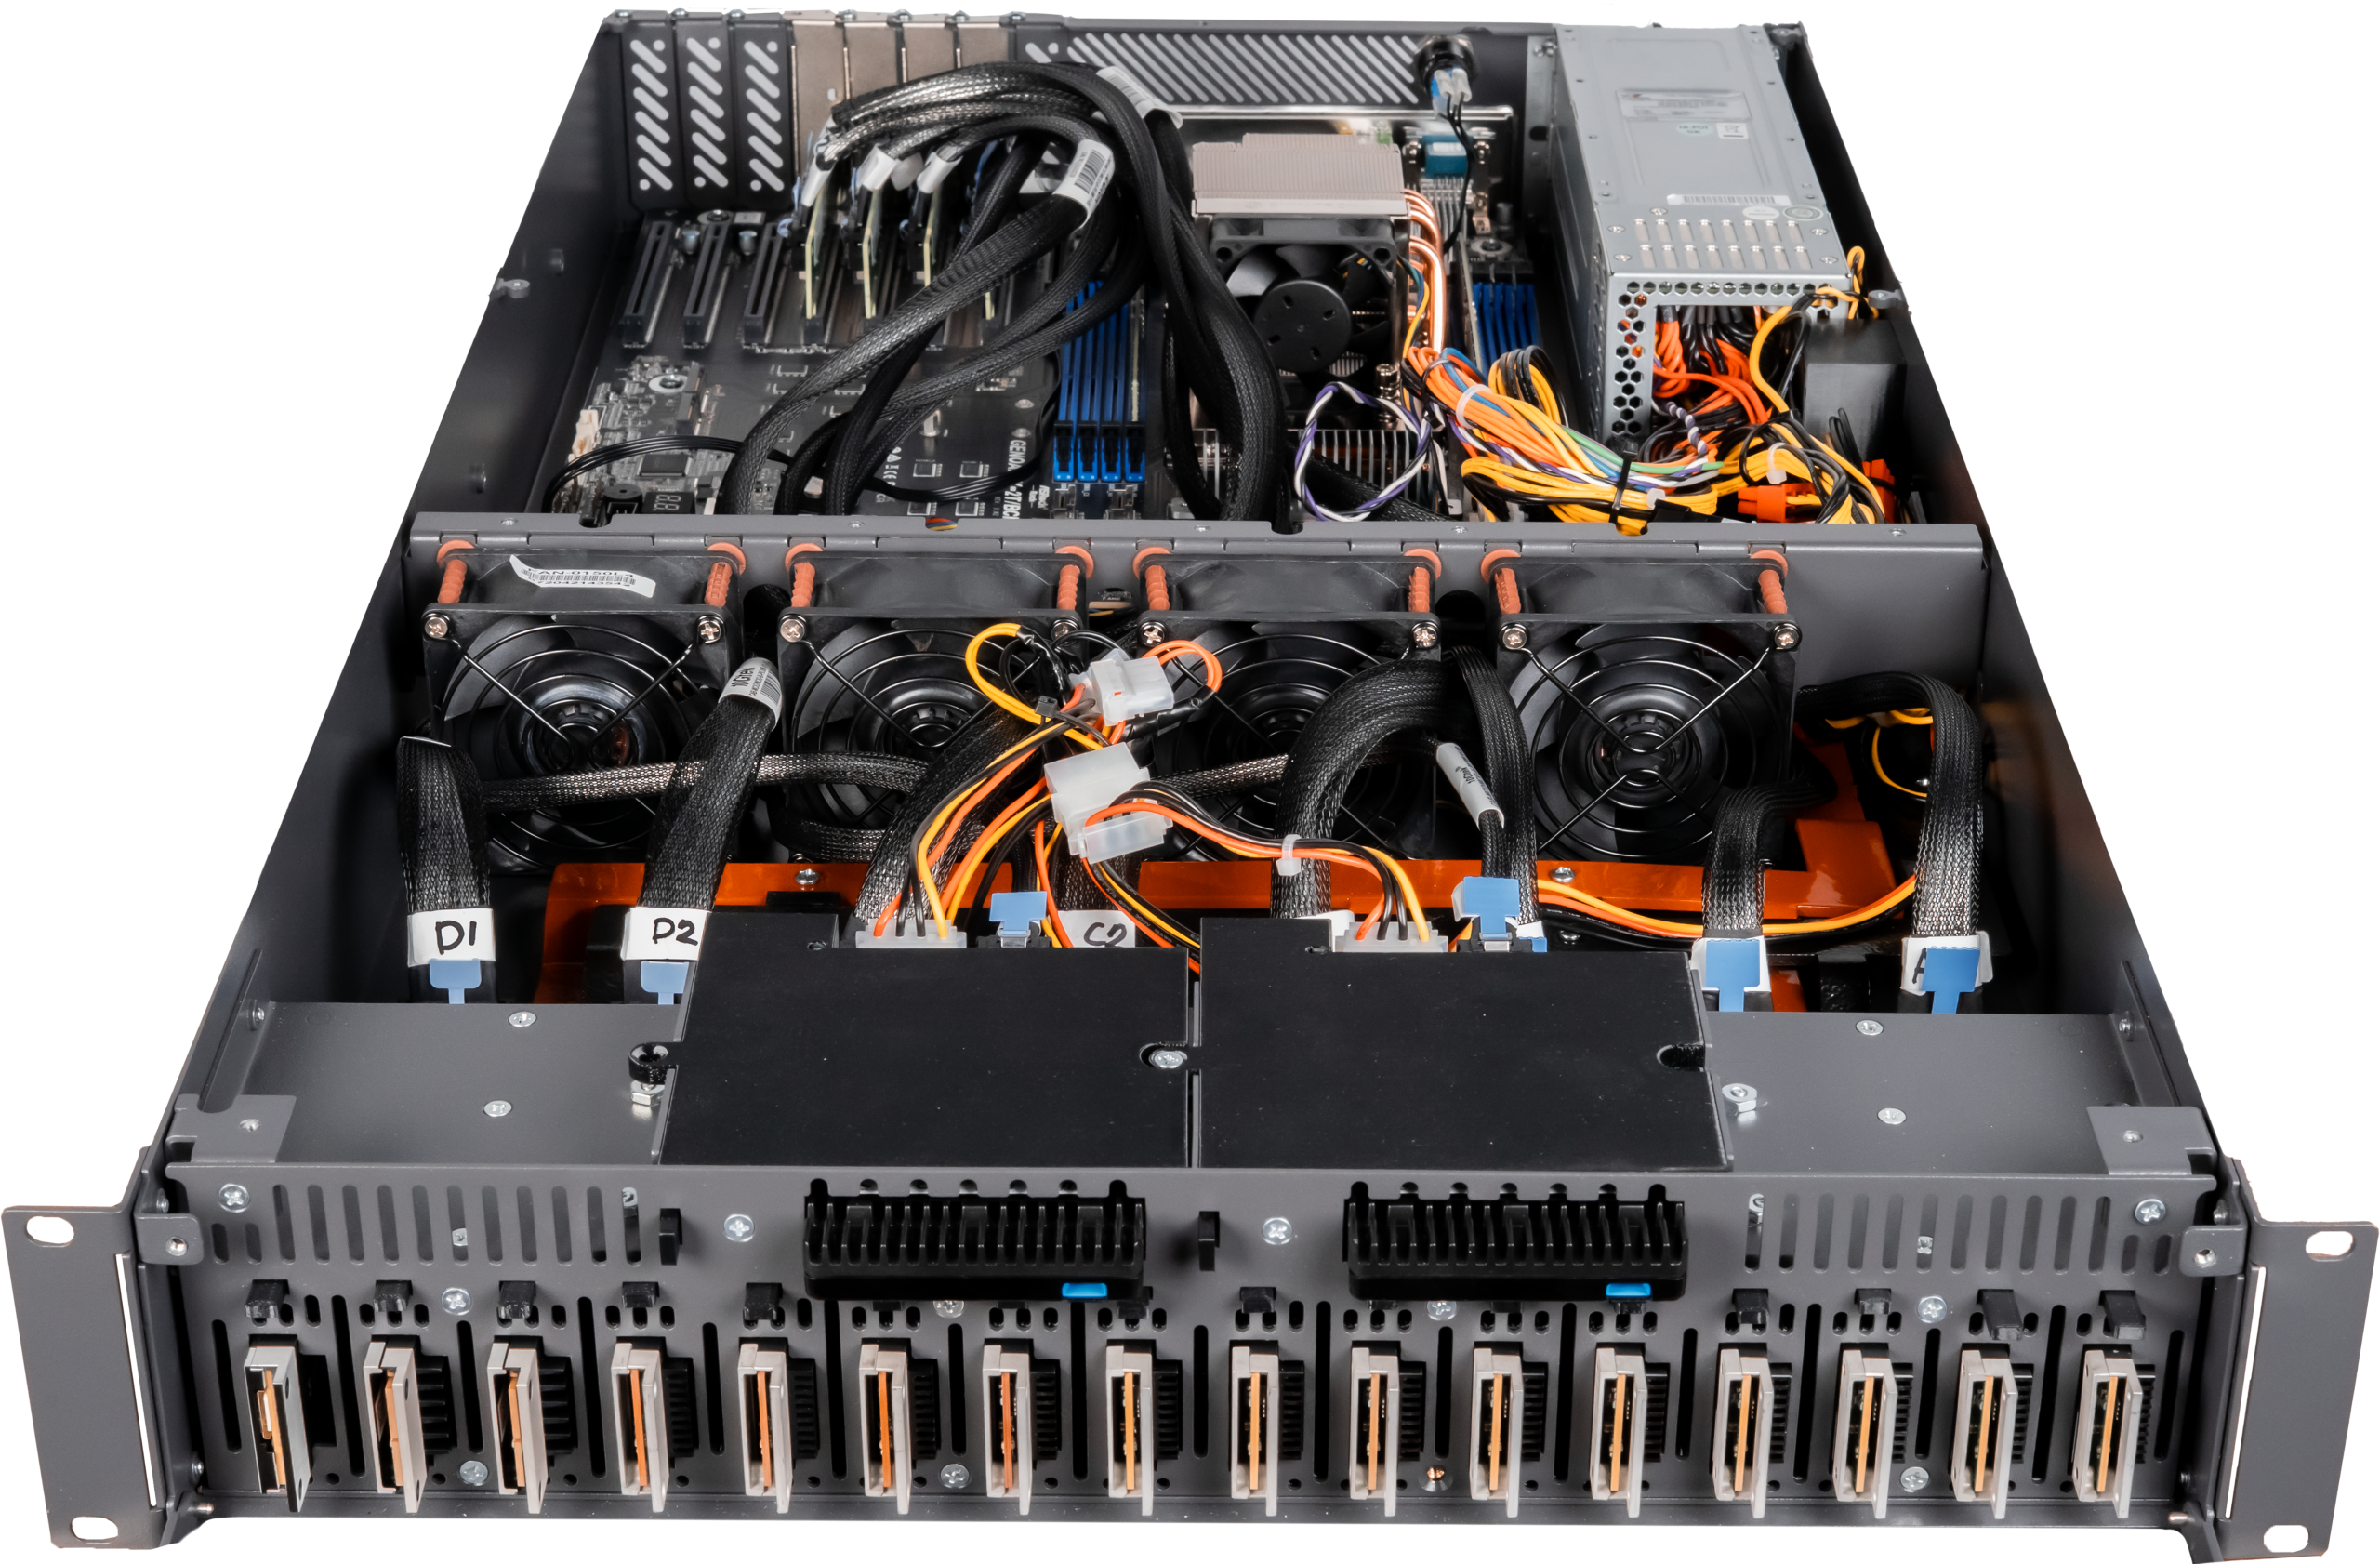
Open-source data storage provider 45Drives Ltd. today announced an expansion of its SnapShield cybersecurity platform that adds protection against data exfiltration and centralized management across multiple servers and locations.
The maker of high-density storage devices positions SnapShield as a last line of defense against ransomware, intercepting malicious payloads before they can corrupt enterprise data. SnapShield runs directly on storage servers, where it analyzes file activity for suspicious behavior. Once activity reaches configured thresholds, it can sever the suspected user’s or client’s connection while allowing unaffected systems and users to continue operating.
45Drives said its approach is intended to complement firewalls, endpoint security, network monitoring and backups rather than replace them. Because SnapShield is agentless, customers don’t have to install software on every workstation.
“The storage servers is an excellent point to add a new layer of defense,” said founder Douglas Milburn.
The new Data Exfiltration Protection capability extends behavioral analysis beyond encryption to detect signs of exfiltration, which typically involves repeated file reads followed by data moving outward.
SnapShield watches for unusual patterns such as spikes in file access and interaction with sensitive-looking “honey files” planted as decoys. If activity passes a specified threshold, the platform can notify administrators or automatically isolate the offending user or IP address.
45Drives developed SnapShield after it suffered a ransomware attack launched through a socially engineered email. Although backups were available, Milburn said identifying affected computers and determining which files to restore was disruptive and time-consuming. That experience led the company to look for a way to stop attacks closer to their intended target.
SnapShield also includes Precision Restore, which identifies files affected during an attack so administrators can roll back damaged data selectively rather than restore an entire environment. Milburn said containment can be triggered by activity across just a few files, limiting damage in environments that may hold hundreds of thousands or millions of files.
“The objective is containment,” he said. “If something malicious gets through the traditional defenses, we want to stop the compromised system from continuing to damage or access the data.”
SnapShield supports Rocky Linux and Ubuntu deployments, including single servers and multinode Ceph clusters installed with an Ansible playbook. Real-time email and system notifications are designed to keep administrators informed as suspicious events unfold.
Milburn acknowledged that legitimate activity can occasionally produce a false positive and noted that administrators can temporarily disable protection for specific users or periods when maintenance or another unusual task might resemble malicious behavior.
The second major addition, the Centralized Management System, addresses the difficulty of administering SnapShield on a server-by-server or cluster-by-cluster basis. It provides a single console for viewing deployments, active events, user activity, analytics and audit logs, allowing administrators to drill into an affected system. The capability is aimed particularly at large enterprises and managed service providers overseeing multiple sites or customer environments.
Support our mission to keep content open and free by engaging with theCUBE community. Join theCUBE’s Alumni Trust Network, where technology leaders connect, share intelligence and create opportunities.
Founded by tech visionaries John Furrier and Dave Vellante, SiliconANGLE Media has built a dynamic ecosystem of industry-leading digital media brands that reach 15+ million elite tech professionals. Our new proprietary theCUBE AI Video Cloud is breaking ground in audience interaction, leveraging theCUBEai.com neural network to help technology companies make data-driven decisions and stay at the forefront of industry conversations.