 AI
AI

AI

As artificial intelligence agents move from experimental tools into production systems, enterprise governance is being forced to answer a harder question. It is no longer enough to know what an agent did. Organizations increasingly need to prove what the agent was authorized to do, why it was allowed to take a specific action and whether that authority remained intact as tasks moved across multiple agents and systems.
That challenge is becoming more urgent as agentic systems spread across regulated enterprises, where security, auditability and sovereignty requirements can limit reliance on external software-as-a-service control planes.
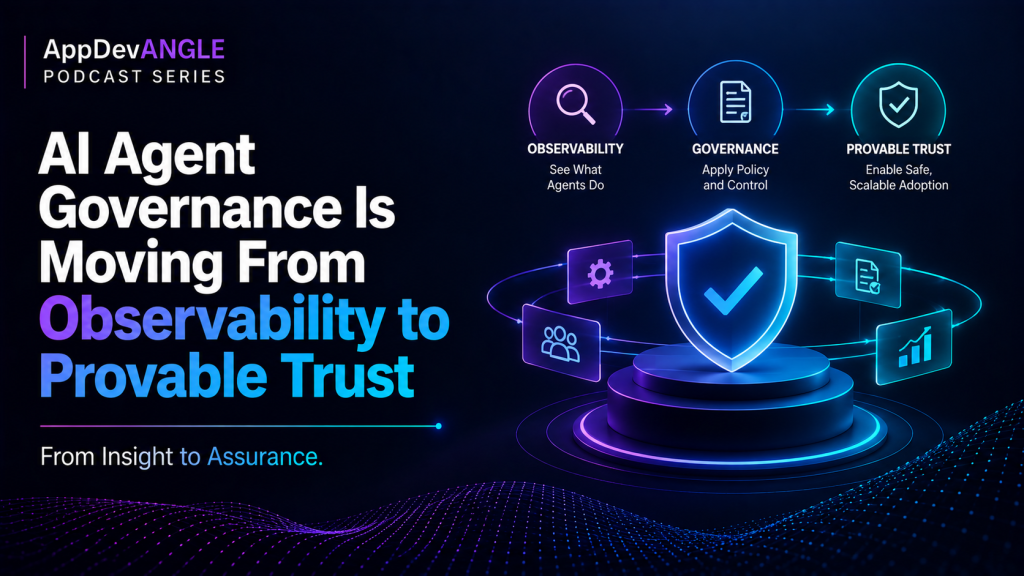
In the latest episode of theCUBE Research’s AppDevANGLE podcast, I spoke with Sudeep Goswami, chief executive officer of Traefik Labs Inc., and Andreas Prins, who leads sovereignty strategy at SUSE Group, about how AI governance architectures must evolve as autonomous agents begin making decisions and delegating work across increasingly complex enterprise environments.
“When you have an agent that is handing a task to another agent, that authority should shrink and not leak out,” Goswami said.
Enterprise observability has traditionally focused on reconstructing what happened after an event. Logs, traces and dashboards can show which systems were involved and where a failure occurred.
Agentic AI introduces a different governance problem.
An autonomous system may receive authority from a human, delegate a task to another agent, invoke a tool or application programming interface and then pass part of that task to another system. Every step potentially changes the scope of what is authorized.
That means identity and credentials alone are insufficient.
“Just because an agent has some credentials, is that agent allowed to make this specific action right now, given the surrounding context around it?” Goswami asked. “A simple credential cannot answer that.”
The challenge is similar to physical access control. An employee badge may authorize entry into a building, but that does not automatically grant permission to approve a financial transaction or access every system inside the organization.
AI governance therefore needs to become contextual. Policies must determine what an agent can do based not only on its identity, but also on the task, environment, delegation chain and operational conditions surrounding the request.
That shift changes governance from post-event reconstruction toward real-time authorization and proof.
The complexity increases when agents begin delegating work to other agents.
Traditional enterprise access models were designed largely around humans, applications and predefined service accounts. Agentic systems introduce a chain of machine-to-machine interactions where authority can move across orchestrators, subagents, APIs and tools at machine speed.
Prins compared the shift to the evolution of continuous integration and continuous delivery systems.
Years ago, software teams moved from manual production releases toward automated pipelines. That required organizations to codify approvals, security checks, secrets management and release policies directly into the delivery process.
Agentic AI may require a similar transition.
“We go through that same thinking again,” Prins said. “Let’s rethink, and more importantly, let’s articulate as code.”
That becomes especially important as the number of enterprise agents grows.
Prins described a recent conversation in which one executive discovered that an engineering organization had created approximately 8,000 agents.
“If you’re unaware how many are created, you are also unaware what they’re doing and what their function is,” he said.
The implication is that agent proliferation could quickly outpace traditional governance models. Enterprises may eventually need the equivalent of software supply chain controls for agents: explicit identity, delegated authority, policy enforcement and evidence showing how each system behaved.
Defining policies is only one part of the problem. Enterprises also need mechanisms capable of enforcing those policies where agents actually interact with applications and infrastructure.
That puts the gateway layer in an increasingly important position.
Goswami argued that AI governance systems need to capture both allowed and denied actions. Showing that a system successfully blocked an unauthorized action can be just as important as showing that an authorized task completed correctly.
“You want to be able to showcase proof that your guardrails are working,” he said. “Which means it should allow and deny, and you want to have that entire thing in context.”
The enforcement layer can also provide a feedback loop into governance policies themselves.
If agents repeatedly attempt actions that are denied, that information may reveal poorly designed workflows, overly permissive instructions or gaps in the policy framework.
The result is a governance model where policy definition, enforcement and evidence become interconnected rather than operating as separate security functions.
Logging has long formed the foundation of enterprise auditing, but autonomous AI introduces another trust problem: the system producing the evidence may also control that evidence.
Goswami compared the issue to a vehicle odometer. If the owner of the vehicle can modify the mileage and is also the only party reporting the mileage, there is no independent way to verify whether the record has been altered.
The same issue can occur with audit logs generated by applications and vendors.
“They can be tampered with, and there’s no third-party way to know when and how it was tampered,” Goswami said.
Cryptographic evidence can strengthen that trust model by making changes detectable. Instead of relying entirely on conventional logging, systems can cryptographically record decisions, authorization results and agent actions.
But cryptographic signing alone does not completely solve the problem.
Goswami argued that enterprises also need independent verification capable of determining whether evidence has been modified after it was generated.
“You need the logging capability at a cryptographic level, but then you also need a third-party verification mechanism to be able to check against it,” he said.
That turns observability data into something closer to verifiable evidence.
For highly regulated environments, the distinction could become significant. An organization may eventually need to demonstrate not only what an agent did, but also that its records could not have been altered after the fact.
Governance becomes more complicated when organizations cannot depend on externally hosted control planes.
According to research cited during the conversation, 47% of respondents operate across a mix of connected and disconnected environments, while 11% deploy generative AI specifically within on-premises and air-gapped infrastructure.
That makes sovereign AI more than a regional compliance issue.
Organizations in defense, healthcare, financial services, government and other regulated industries may need to operate models, governance controls and verification infrastructure entirely within environments they control.
“The moment you become dependent on a third-party SaaS service that you don’t control or it’s not in your own soil, then all bets are off,” Goswami said.
Prins described sovereignty as a risk-based decision involving both the model itself and the infrastructure used to operate it.
Organizations can choose between closed frontier models, open-weight models and open-source models. Each involves different tradeoffs around transparency, ease of use and control.
The deployment environment introduces another decision.
Enterprises may consume models through a SaaS provider or run them within infrastructure they manage themselves. The more sensitive the workload and data, Prins argued, the stronger the case becomes for customer-controlled infrastructure.
“The more regulated, the more control you should have,” he said.
The discussion also highlighted why sovereignty is unlikely to be delivered by a single platform.
An enterprise AI stack can include models, CPUs and graphics processing units, Kubernetes infrastructure, gateways, policy engines, observability systems and evidence layers.
Each component plays a different role in determining whether an organization can control and verify its AI environment.
“There is no single vendor that can deliver sovereignty all by themselves,” Goswami said.
That makes interoperability and partnerships increasingly important.
Traefik Labs and SUSE are approaching the problem from different layers of the stack. SUSE provides underlying infrastructure and open-source technologies, while Traefik provides gateway and agent governance capabilities.
Goswami described a sovereign architecture that combines open-weight models, customer-controlled compute infrastructure, gateway-based controls, observability and an evidence or provenance layer capable of verifying agent behavior.
The broader goal is to make agentic systems easier to adopt without separating security and governance from the architecture supporting them.
“The objective is to ensure that there is a high degree of secure and scalable adoption of agentic workflows in the enterprise,” he said.
AI governance is rapidly moving beyond dashboards and retrospective audit logs.
As autonomous agents begin invoking APIs, delegating tasks and taking action across enterprise systems, organizations will need to understand not only what happened, but what authority existed at every point in the process.
That creates new architectural requirements around contextual authorization, policy enforcement, machine-to-machine identity and verifiable evidence.
Sovereignty adds another layer. For organizations operating in regulated, disconnected or air-gapped environments, governance capabilities may need to run entirely within customer-controlled infrastructure.
The result is a shift from observability toward provability.
Enterprises adopting agentic AI will increasingly need architectures capable of answering four questions: Which agents are operating? What authority do they have? Were they permitted to take a specific action in context? And can the organization independently prove what happened afterward?
The companies that answer those questions early will be better positioned to scale agentic systems without losing control of the authorization, governance and trust models underneath them.
Here’s the complete conversation with Traefik Labs’ Sudeep Goswami, SUSE’s Andreas Prins and me, part of theCUBE Research’s AppDevANGLE podcast series:
Support our mission to keep content open and free by engaging with theCUBE community. Join theCUBE’s Alumni Trust Network, where technology leaders connect, share intelligence and create opportunities.
Founded by tech visionaries John Furrier and Dave Vellante, SiliconANGLE Media has built a dynamic ecosystem of industry-leading digital media brands that reach 15+ million elite tech professionals. Our new proprietary theCUBE AI Video Cloud is breaking ground in audience interaction, leveraging theCUBEai.com neural network to help technology companies make data-driven decisions and stay at the forefront of industry conversations.